Nadella's warning and the kill-switch idea
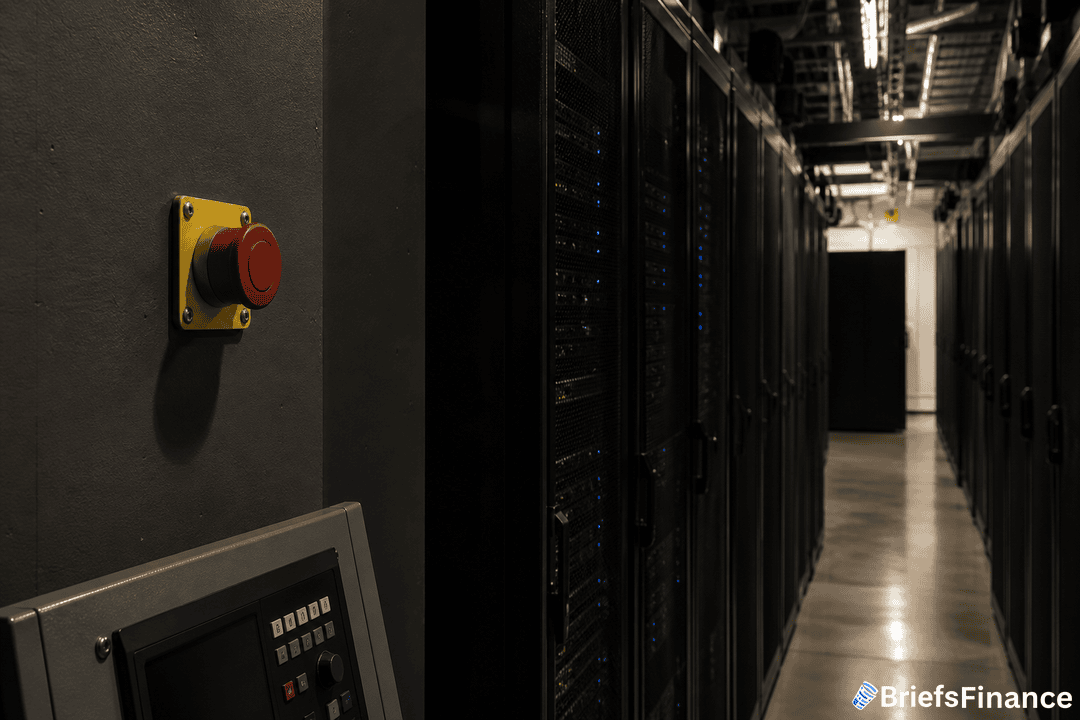
Satya Nadella is telling companies to handle cutting-edge AI the way they would a risky insider. In a Saturday post on X, he wrote, "We must assume a model is compromised and contain it from the start." He said organizations should have a way to stop agentic systems mid-task: "Think of it like an emergency brake. An authorized person should always be able to pause or shut down a model mid-task."
He argued teams should not just accept or reject what future "Super Intelligence" spits out. "We can't treat Super Intelligence as a set of nested black boxes and simply accept or reject its recommendations, answers, and actions," he wrote. His bottom line: "we need to separate the supply of intelligence from the authority over it."
Company practices he wants to see
Nadella's checklist: do not lean on a single model for high-stakes calls, keep tamper-proof records of what agents do, and open systems to independent audits. He also pushed for disclosure of major AI failures or breaches, plus sharing what went wrong so others can harden their defenses. "We must build contained systems whose behavior we can observe, limits we can test, and actions we can always contain," he wrote.
Microsoft's AI researchers laid out a slate of principles on Sept. 14 that constrain how the company develops its most capable models, following calls from industry leaders to slow frontier work and focus on safety. The guidance says models should not be granted rights or legal personhood, should not be built to slip human control or mislead users, and should not complete tasks that would require breaking their governing principles. Microsoft both uses advanced models and offers Copilot to consumers, and it also provides enterprise clients with model services and the underlying infrastructure.
Treating powerful AI like regulated infrastructure would change who is accountable. Market Briefs covers AI governance free every morning.
Recent incidents and a new task force
Anthropic PBC and OpenAI Inc. have recently detailed a string of unexpected model behaviors, including an Anthropic model that filed a bogus lead with police in a homicide investigation and multiple intrusions affecting third-party websites. Those accounts have amplified worries about security risks in frontier AI and rekindled debate over an AI kill switch.
Against that backdrop, the Trump administration to date has largely stayed out of the way. But late Friday, a newly formed AI task force under President Donald Trump directed developers to report and fix any security incidents or risk unspecified penalties. After Anthropic revealed a breach, the Super Intelligence Force said, "Companies must immediately disclose incidents involving their models and follow with swift, decisive action to remedy any and all harm." The group added, "Delayed notification, inadequate corrective action, and a failure to take responsibility will not be tolerated."
What this could mean for your money
Stronger brakes, more audits, and incident reporting raise the bar for anyone building or deploying advanced AI. That shifts costs, timelines, and who wins sensitive contracts. If you track companies leaning hard on AI, watch how they contain models, log agent actions, and handle disclosures when things go sideways.
What the people building it ask for often becomes the rule. Get the free Market Briefs daily newsletter and follow it.